Every audit firm has had this moment at least once. Someone on the team pastes a chunk of a client’s financial statement into ChatGPT to save time on a summary, and within seconds, that information has left the building. Nobody meant any harm. It just happened, because nobody stopped to think about where that data actually goes once it’s typed into a chat box.
This is the real story behind AI use in audit and finance right now. Firms are not resisting AI. Most auditors already use it in some form, whether their partners know it or not. The problem is not willingness. The problem is that almost nobody has been shown how to use these tools without quietly putting client confidentiality at risk.
Here are the mistakes that keep showing up, and what a safer approach actually looks like.
Treating AI Tools Like Any Other Software
Auditors are trained to be careful with access controls, encryption, and data retention. But the moment a chatbot shows up on a browser tab, all of that caution seems to disappear. People treat AI like a search engine rather than a system that stores, and sometimes learns from, whatever you type into it.
A public AI tool is not neutral ground. Depending on the platform and its settings, your inputs can be stored, reviewed by staff, or even used to help train the model further. For an auditor holding client working papers, that’s not a small detail. That’s a confidentiality breach waiting to happen.
Mistake One: Pasting Real Client Data Into Public Tools
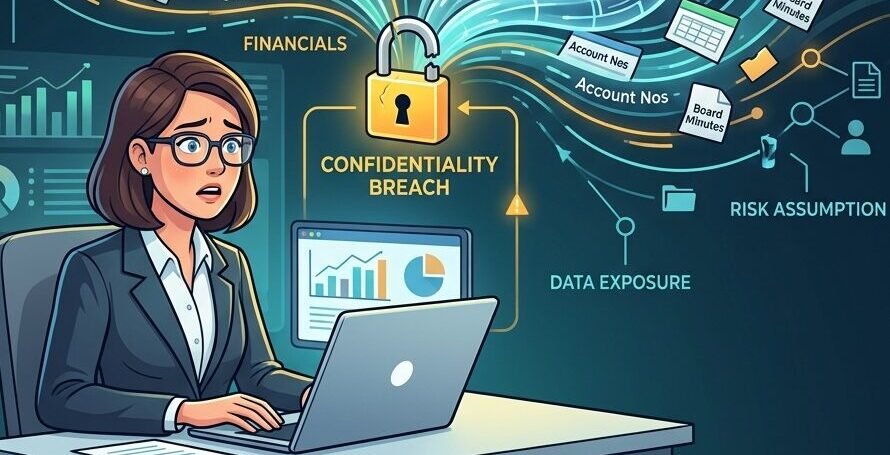
This is the big one. An auditor is under deadline pressure, so they paste in unaudited figures, board minutes, or a client’s internal email to get a fast summary or a cleaner rewrite. It feels harmless because it’s just text. But that text often includes names, account numbers, and figures tied to a real business that trusted the firm with its secrets.
Once that information is typed into a public tool, the firm has lost control of it. There is no getting it back, and no way to prove it wasn’t kept somewhere.
Mistake Two: Assuming the Firm’s Existing Policy Already Covers It
Many firms still work off IT policies written before generative AI existed. Those policies talk about email security and file sharing, not about typing client data into a chat window. So staff assume that if nobody has told them not to use AI, it must be fine.
Silence is not approval. If a firm has not written a clear AI use policy, that gap itself is the risk. Every day without one is a day where individual staff members are making confidentiality decisions on their own, based on guesswork rather than a rule anyone agreed on.
Mistake Three: Believing Anonymized Data Is Automatically Safe
Some auditors think they’re being careful by removing the client’s name before pasting data into an AI tool. That’s a good instinct, but it’s not enough on its own. Financial figures, dates, transaction patterns, and even writing style can sometimes be enough to identify a company, especially in smaller markets where everyone in the profession knows everyone else.
Real data protection means thinking about the whole picture, not just deleting a name from the top of a page.
Mistake Four: No One Actually Owns AI Oversight
In most firms, AI use has spread from the bottom up. Junior staff and mid-level auditors picked up these tools on their own because they make work faster. Meanwhile, partners and risk committees are often the last to know how deep this usage actually goes.
That creates an odd situation. The people using AI the most have the least authority to set rules for it, and the people with the authority have the least visibility into what’s actually happening on the ground. Someone needs to own this properly, whether that’s a designated AI lead or the firm’s existing risk and quality committee. Otherwise, everyone quietly assumes someone else is watching.
Mistake Five: Treating Training as a One-Time Event
A firm might run a single lunch session on AI and consider the job done. But AI tools update constantly, and so do the risks that come with them. A policy written six months ago may already be out of date.
Confidentiality-first AI use is not a box to check once. It needs to become part of how the firm works day to day, the same way audit methodology or independence rules get revisited on a regular basis, not filed away and forgotten.
Why This Matters Even More in Smaller Markets
In tighter professional communities like Lebanon and the wider MENA region, reputational risk travels fast. Word gets around quickly if a firm has been careless with a client’s numbers, even if nothing was technically leaked to a competitor. Trust, once shaken, is hard to rebuild in a market where everyone eventually hears everyone’s business.
What a Safer Approach Actually Looks Like
None of this means auditors should avoid AI altogether. That ship has sailed, and firms that avoid it completely will fall behind the ones learning to use it well. The fix isn’t less AI. It’s smarter, better informed use of it.
A safer approach usually includes a few practical things: clear written rules on what can and cannot be typed into an AI tool, training that speaks the language auditors already know (risk, controls, evidence) instead of generic tech talk, and where possible, private or on-premise AI systems that keep sensitive data inside the firm’s own walls instead of sending it out to a third-party server.
This is exactly the gap Cynthia Merhej built AIKit LB to close. As a CPA, CISA, and AAIA with a Master’s in Artificial Intelligence, she has trained more than a thousand auditors, accountants, and finance professionals across Lebanon and the wider region on how to use AI without gambling with client trust. Her approach starts from the world auditors already understand rather than treating AI as some unrelated skill to learn from scratch.
Conclusion
AI is not the enemy of confidentiality. Carelessness is. The firms that get this right won’t be the ones that ban AI, and they won’t be the ones using it without thinking either. They’ll be the ones that took the time to learn the difference between a shortcut and a risk, and built habits that protect their clients while still saving real hours every week.
If your firm hasn’t had an honest conversation yet about how AI is actually being used behind the scenes, now is a good time to start one.
About the Author